Interfeys
UI · vəziyyətlər
Service
API, authentication, data, and interface in one cut. The back of the frontend is not empty — the product looks complete from a distance and works up close.
One team, one responsibility: the same plan from screen to database. The “UI is ready, backend later” gap is closed.
UI · API · Data
Autentifikasiya + rollar
DEMO DATA
Ekran · Müqavilə · Verilənlər
Ekrandan bazaya. Bir kəsim, bir məsuliyyət.
API müqaviləsi
v1 · REST
Who it fits
Product teams
Those who want to turn an MVP or an existing showcase into a real application — API + UI together.
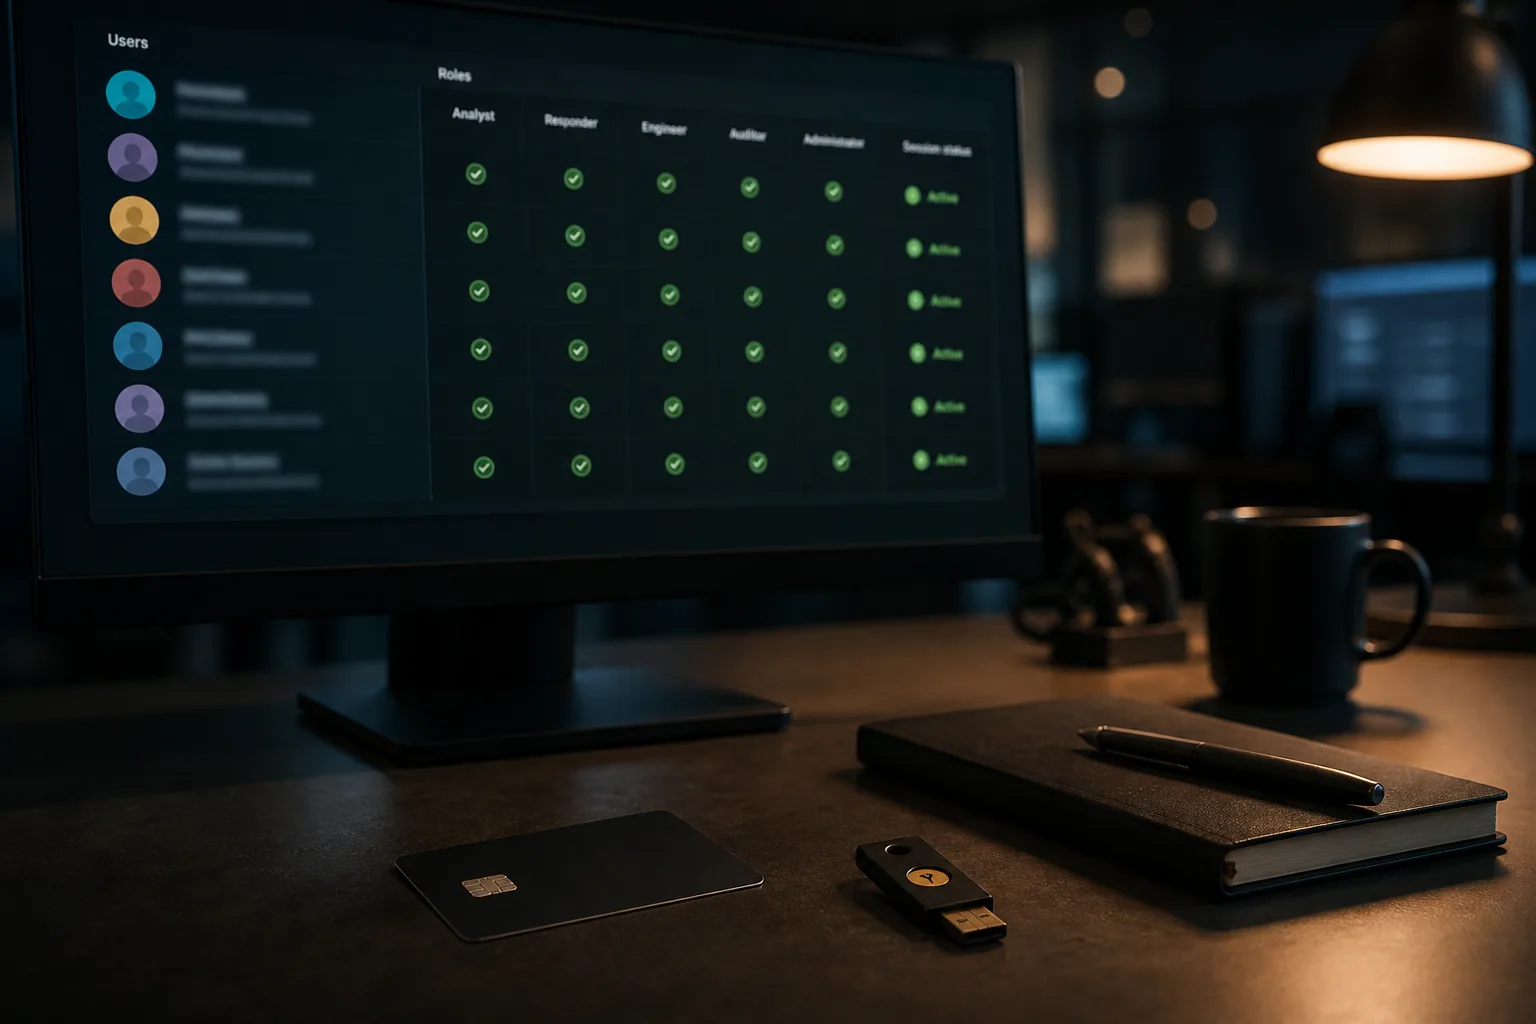
Internal company systems
Those who need a portal, a panel, and integrations; a “pretty page” is not enough.
Those working with an existing stack
Those who want to connect to a ready API or database, but to bind interface and permissions professionally.
Arxitektura
Əvvəl sərhəd, sonra ekran. Interfeys, API və verilənlər ayrı yaşasa da, bir kəsimdə bağlanır — boş mock yox, işləyən dilim.
Ekran işləyir, çünki arxası var.
Interfeys · UI · vəziyyətlər
REST, səhv, versiya — yazılı.
Müqavilə · API · JWT
Sxem, miqrasiya, icazə sərhədi.
Verilənlər · SQL · RBAC
Interfeys
UI · vəziyyətlər
Müqavilə
API · JWT
Verilənlər
SQL · RBAC
Use cases
A project does not need all of them. The cut is chosen for your need — then growing stays easy.
Customer portal + API
Müştəri portalı
Login, profile, request, and status — UI in the browser, a reliable service layer behind it.
Admin panel
Autentifikasiya
Admin
12
Tam
Operator
48
Yazı
Müştəri
214
Oxu
JWT · RBAC
POST /v1/auth
GET /v1/session
200 · exp 3600s · 18ms
List, filter, edit, and report. The frontend is not only a table — real operations.
A bridge to an external system
REST explorer
Request
Authorization: Bearer
Accept: application/json
Response
{ "role": "admin",
"exp": 3600 }
Payment, email, CRM, or ERP APIs are connected with a safe boundary.
Completing an existing UI
Domen + CRUD
İstifadəçi
id · email · rol
274
Sifariş
id · status · owner
1.8k
İcazə
rol · səth · scope
36
Design or frontend exists, but there is no backend — data and auth are added.
Problem
When only the interface is ready, the product stops: where is data stored? Who can see what? How are payment, email, or CRM connected? When frontend and backend move by separate hands, integration is late, permissions stay weak, and every change becomes double cost. Result: a nice screen, an empty system.
Solution
REST API, role-based access, the data model, and the application layer are designed together. Domain and permission boundary first, then the interface. Result: a reliable API, clean data, and a UI that works against it — in the same cut, with the same discipline.
Paralel quruluş
Backend və frontend eyni planda. Boşluq qalmır.
Outcome
01
No empty backstage
The screen takes data from a real source: authentication, CRUD, and business rules work.
02
Who can do what is clear
With a role and permission model: admin, operator, and customer are safely separated in the same system.
03
An API ready for integration
Mobile, PWA, or third-party services can connect to the same contract.
04
Maintainable code
Type safety, clear module boundaries, and documented flow — growing later stays easy.
Session · rol · eyni müqavilə, telefonda
Process
01
Discovery
We clarify business rules, user roles, existing systems, and the success criterion.
02
Contract
API, data, and permission boundary are written. Agreement first, then code.
03
Build
Backend and frontend in parallel, but on the same plan. A working slice every sprint.
04
Delivery
Test, security check, deploy, and a short document. Then a measured next step.
Delivery
Difference
One chain of responsibility
There is no “frontend ready, backend is someone else’s job”. The gap does not stay in your product.
Boundary first, then the screen
Permissions and the data model are clarified early — then the UI is bound quickly and safely.
Honest scope
Every integration and module is written in advance. There is no hidden “we will add it later” list.
A short conversation is enough. We clarify the need, draw the path, then make an offer.
Write now — no need to wait for the form.
Write on Instagram